Hi, thanks for your quick reply.
DNSSEC itself in the domain is not the problem.
Once the Windows client is instructed by GPO (Group Policy) e.g. validating mydomain.local via DNSSEC,
does not work on the client a DNS Resolution.
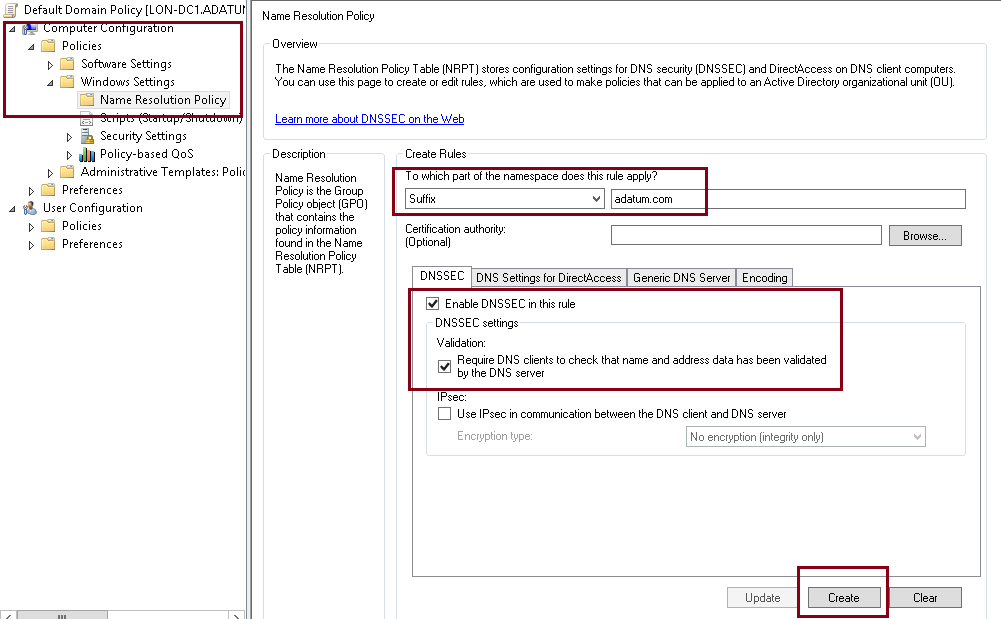
Other VPN clients have no problem with this active GPO.
Once this GPO is disabled, the DNS resolution works fine on the openvpnclient.
So there is a clear link between active DNSSEC validation on the Windows local DNS client (via GPO) and the current openvpn client.
I know routers and also network clients, such as, VPN client have problems with too large UDP DNS packets.
>>Does the domain still resolve when you do it on the command line with ping or nslookup
No, here too there are these problems
>>and does the open source client exhibit the same problem
I will test and report.
