Hello,
I have a problem with my OpenVPN network and I hope you guys can help me out.
I should explain my network first:
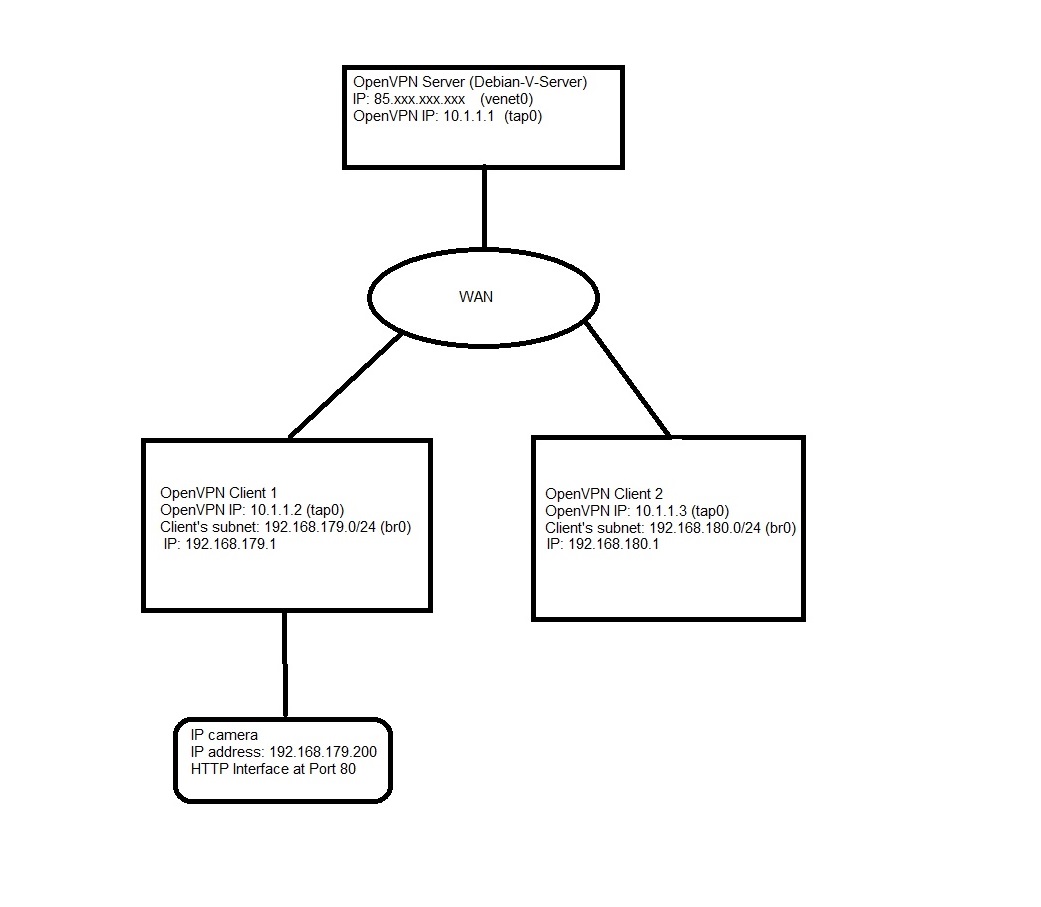
The server itself is hosted on a virtual Debian server and it has 2 clients over WAN connected, an Asus router at home and another one at my office (both Linux devices with Optware).
At home I have a native IPv6 connection to the internet and my provider uses a Carrier-grade-NAT to give me access to IPv4 WAN, which means that my home network is not accessible from the outside.
To get access to my NAS and other services at home I use the OpenVPN connection to route these packages to my virtual Debian Server, what brings me to my problem.
I have a network camera at home and want to access it from the outside with my smartphone over the app "tiny cam", but my camera doesn't support HTTPS, so I'd like to use Stunnel to convert my camera's HTTP interface to HTTPS. So I installed Stunnel on my virtual Debian server and told him to host my camera's webinterface (192.168.179.200:80) at port 4000.
The problem now is, that the OpenVPN server is not able to reach any client or any IP in one of the clients' subnet.
The server isn't even able to reach the clients or the devices in their subnets. When I try to ping one of the clients or a device in their subnet nothing happens, traceroute only shows asterisks.
The other way around everything works fine, both clients are able to access each other, the Debian server and the subnet behind them. (ping and traceroute is also working)
I already tried to play around with iptables, especially with the FORWARDING table, on the server and the clients, but had no success with it,
so I hope somebody of you might have a plan on how to get this working?
Here are my configs:
Server config
ca /etc/openvpn/easy-rsa2/keys/ca.crt
cert /etc/openvpn/easy-rsa2/keys/my.crt
key /etc/openvpn/easy-rsa2/keys/my.key
dh /etc/openvpn/easy-rsa2/keys/dh1024.pem
port xxx
proto tcp
client-to-client
client-config-dir TAPVPNConfig
dev tap
server 10.1.1.0 255.255.255.0
push "route 10.2.1.0 255.255.255.0"
push "route 10.3.1.0 255.255.255.0"
push "route 10.4.1.0 255.255.255.0"
user nobody
group nogroup
persist-key
persist-tun
keepalive 27 79
comp-lzo
tun-mtu 1500
tcp-nodelay
log openvpn.log
topology subnet
With the following commands I added the routes for the subnets to the servers' routing table:
route add -net 198.162.179.0 netmask 255.255.255.0 gw 10.1.1.2 dev tap0
route add -net 198.162.180.0 netmask 255.255.255.0 gw 10.1.1.3 dev tap0
Client 1 specific config (the same for client 2 with adjusted IPs of course)
ifconfig-push 10.1.1.2 255.255.255.0
push "route 192.168.180.0 255.255.255.0 10.1.1.3"
Client 1 config (client 2 uses the same config)
client
proto tcp-client
remote 85.xxx.xxx.xxx xxx
resolv-retry infinite
nobind
dev tap0
ca /etc/storage/openvpn/client/ca.crt
cert /etc/storage/openvpn/client/client.crt
key /etc/storage/openvpn/client/client.key
persist-key
script-security 2
writepid /var/run/openvpn_cli.pid
up ovpnc.script
down ovpnc.script
auth SHA1 # SHA1 160 bit (default)
cipher BF-CBC # Blowfish 128 bit (default)
comp-lzo
nice 3
verb 0
mute 10
